// proof over claims
Published research, visible evidence.
The credibility behind every engagement comes from public vulnerability research, coordinated disclosure and verifiable evidence in AI infrastructure, firmware and cryptography. The same researcher does your monthly AI security testing.
Where the findings landed
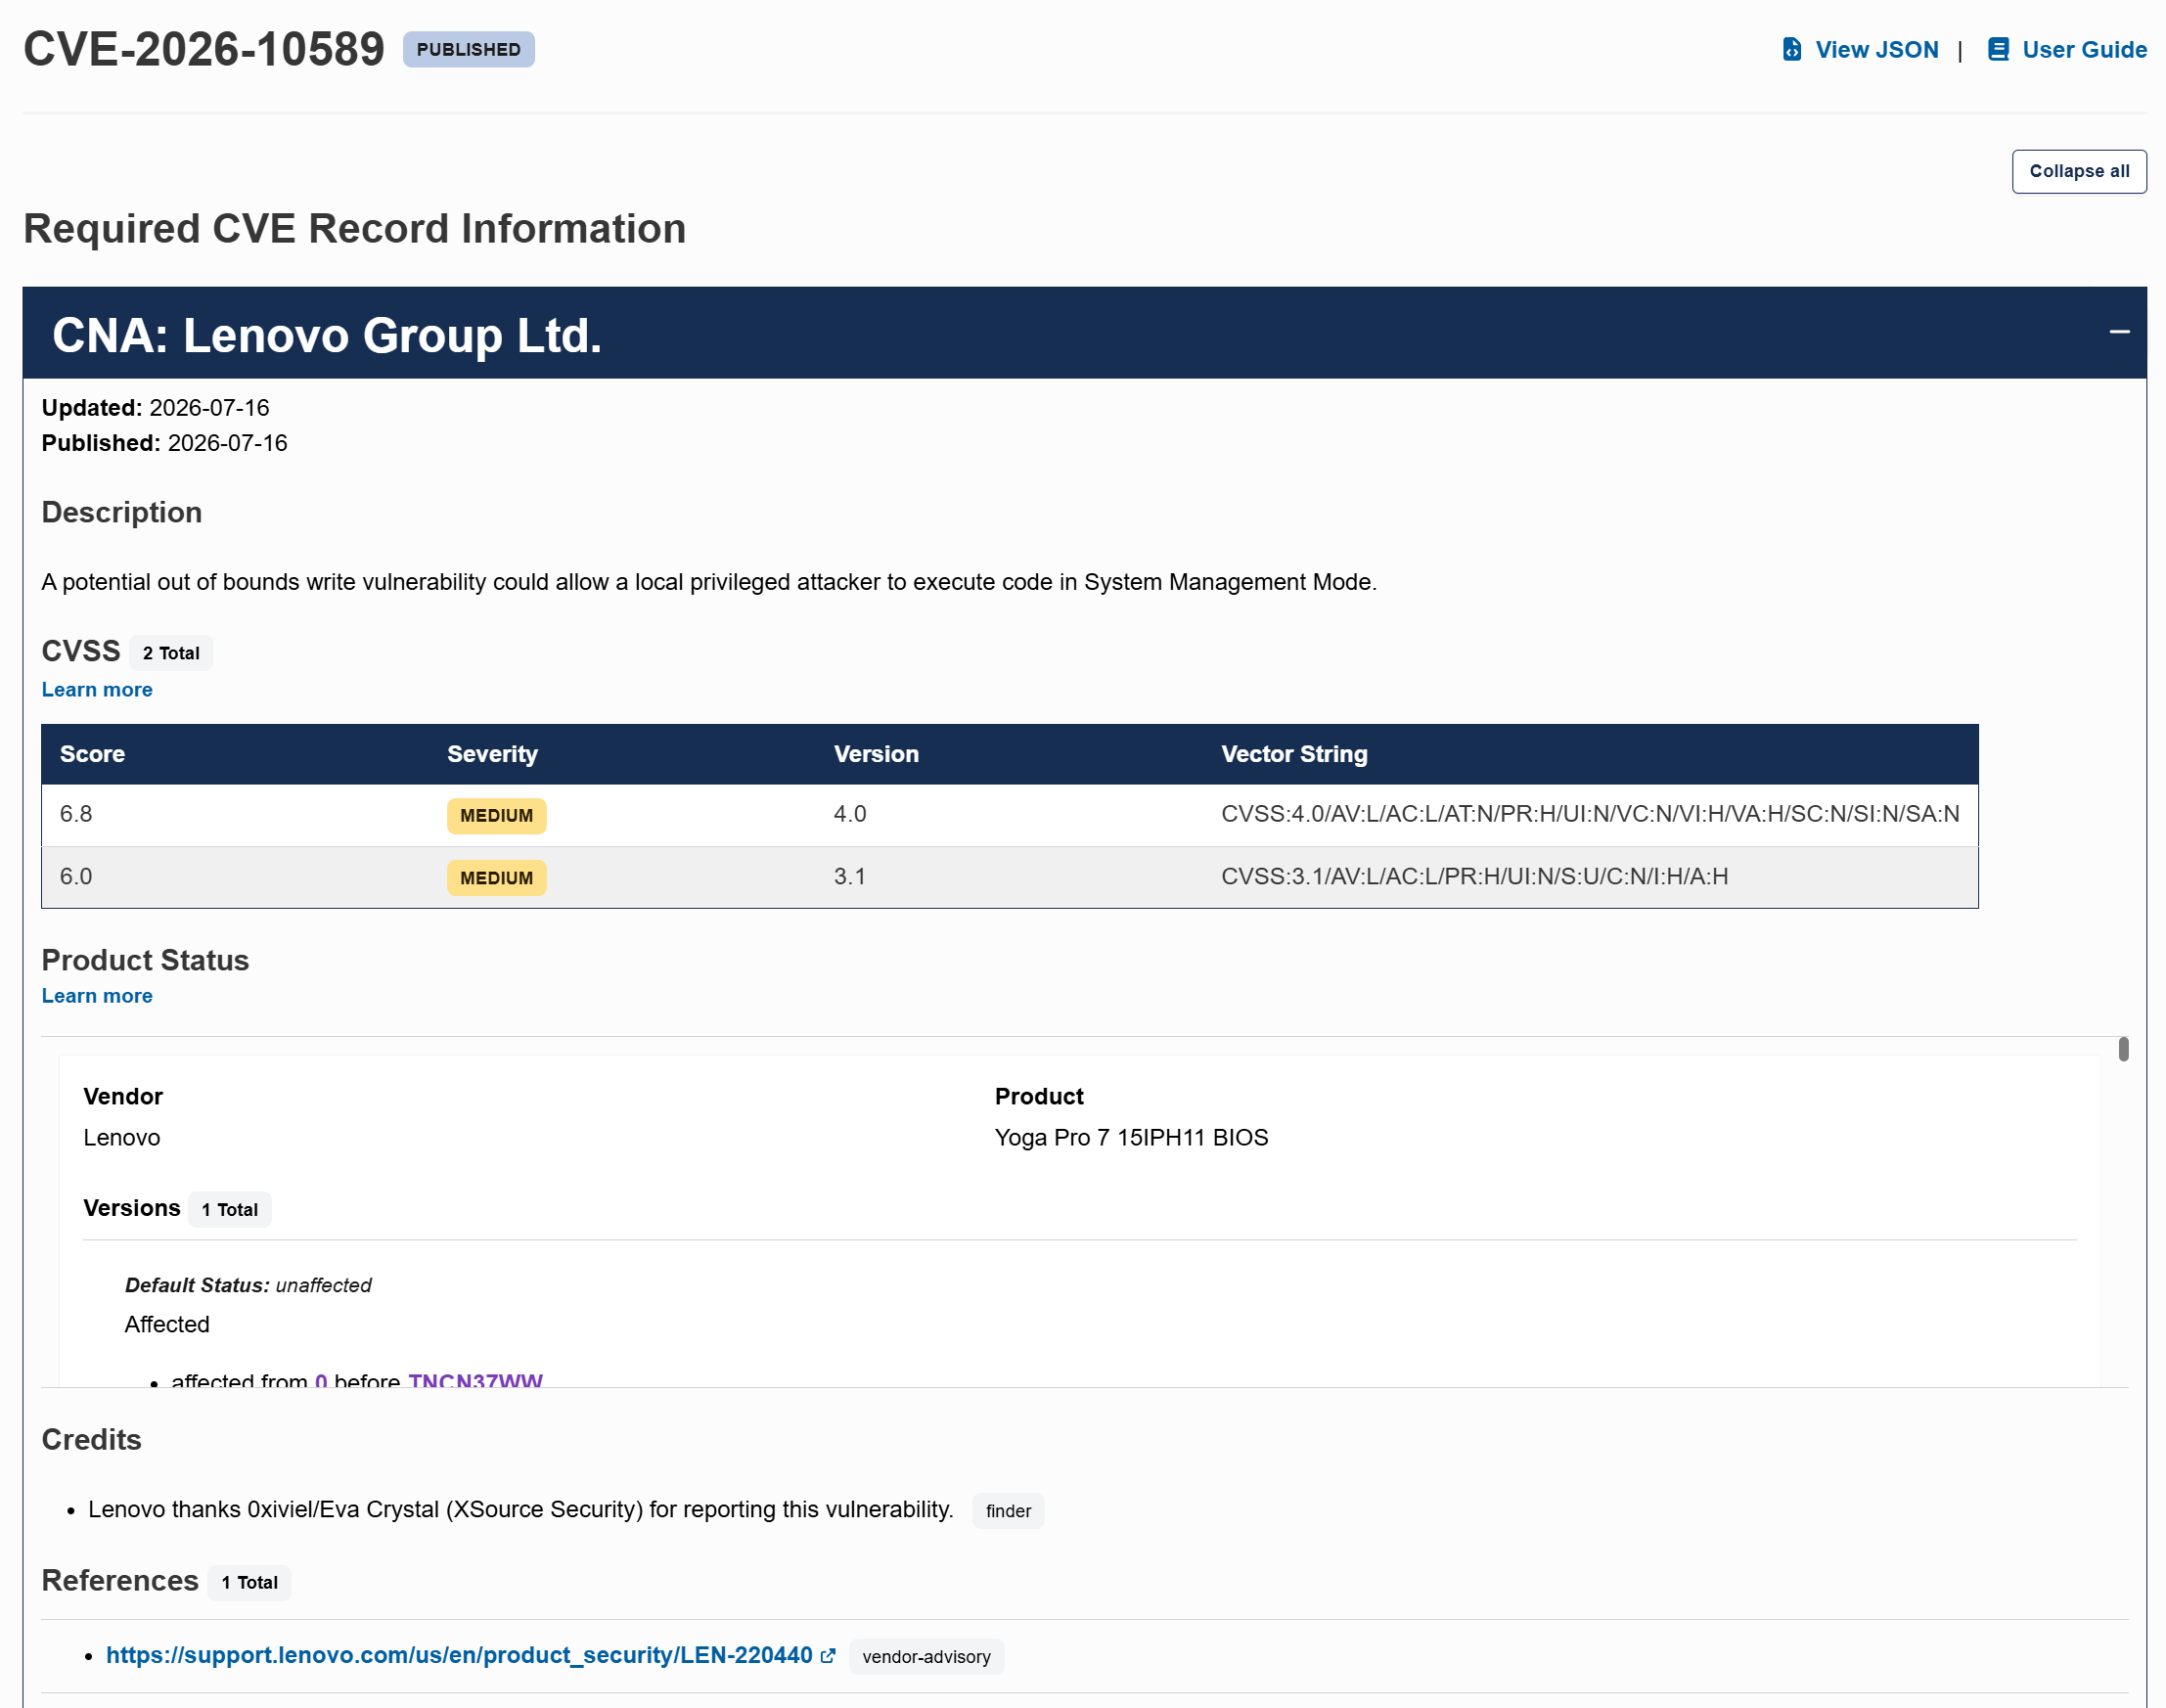
LenovoInsydeH2O BIOS: SMM handler buffer validation, SMRAM address leak, missing handler authentication, ring -2 code execution.4 CVEs
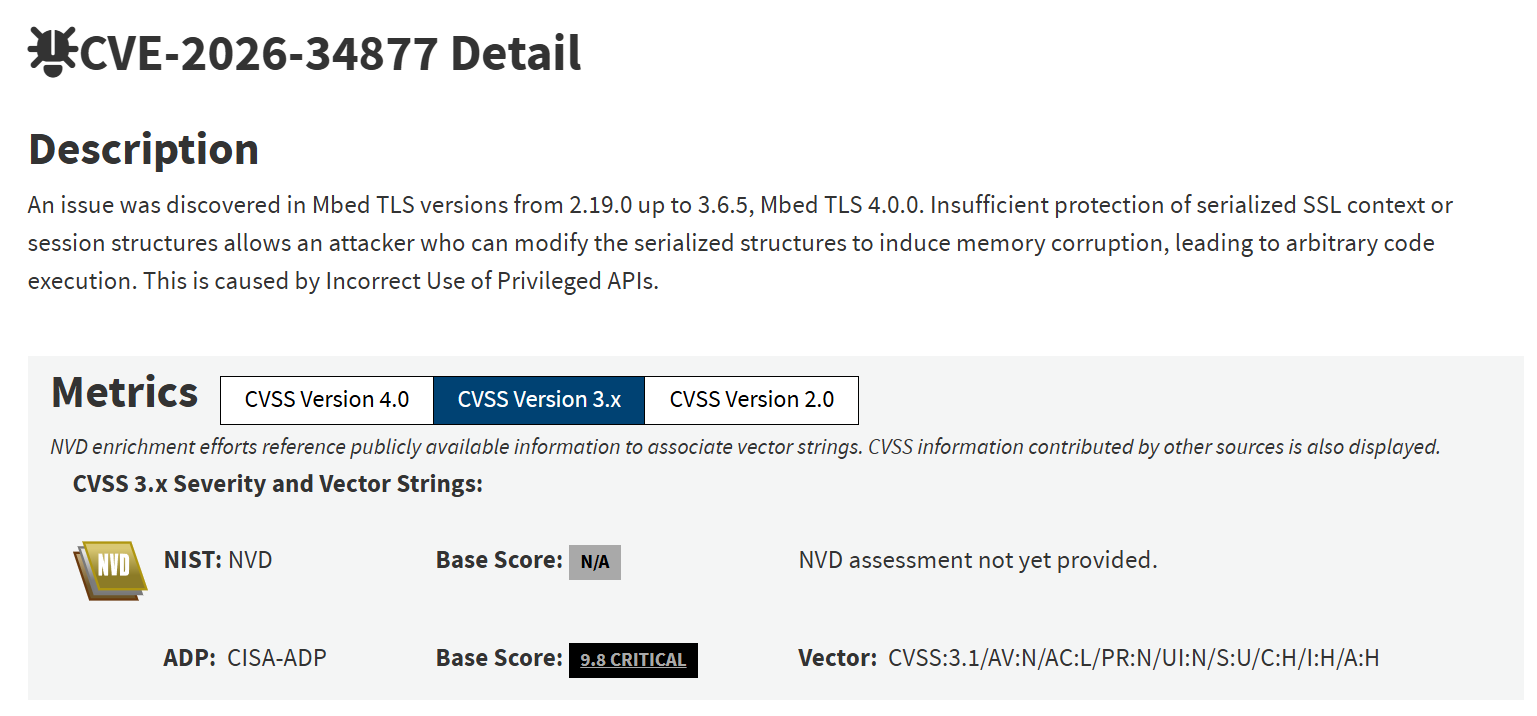
Mbed TLSSerialized-session memory safety, FFDH key handling, CCM out-of-bounds read, ECDH buffer overflow.4 CVEs · up to 9.8
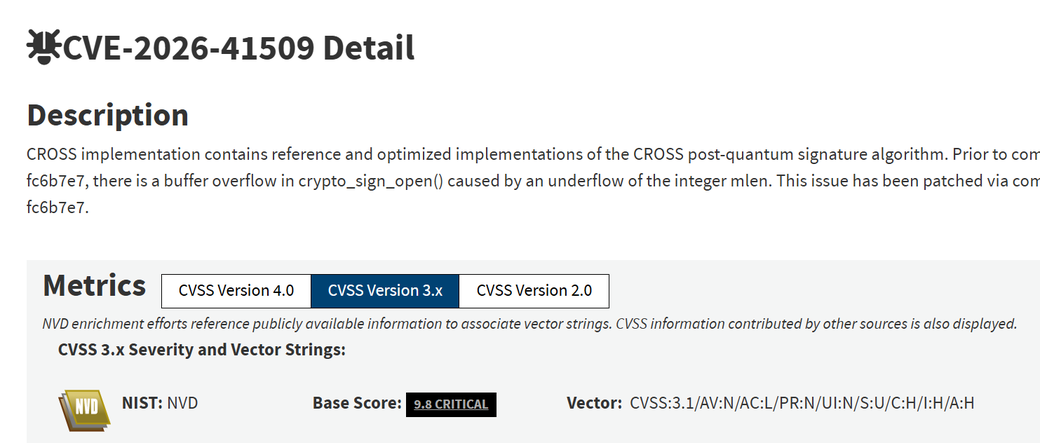
CROSSPost-quantum signature reference implementation: integer underflow to buffer overflow in signature opening.CVE-2026-41509 · 9.8
oqs-providerDouble-free and NULL-check defects in the Open Quantum Safe OpenSSL provider; fixes authored and merged upstream (PR #766, PR #767).2 advisories · fixes merged SNOVAPost-quantum signature reference implementation: lookup tables read before initialization in public-key expansion, and an oversized bound in signature verification; fixes authored and merged into the official source (PR #15).2 fixes merged liboqsLMS stateful signatures: verification did not bind the signature and public key to the parameter set in use. Reported publicly in issue #2568, credited as an independent report in the joint advisory (GHSA-xv6c-h66p-6mfq).CVE-2026-104255 assigned · co-credited Linux kernelaccel/amdxdnaAMD NPU driver: a mailbox channel pointer left dangling after a failed start (use-after-free on the restart path), merged into mainline for Linux 7.4; and an unbounded sync_bo flush range, fixed in the 6.18 longterm branch (Linux 6.18.57). Patches authored.2 fixes merged AMDNPU kernel driver IOCTL out-of-bounds access, buffer overflow, WMI SMI injection, AMDKFD stack out-of-bounds.4 accepted
IntelInteger overflows, OpenVINO deserialization, TensorFlow SavedModel parsing.5 accepted
ARMTrusted Firmware: TF-A, TF-M, OP-TEE and Mbed TLS (SM2 KEP, ECDH overflows, FF-A, PSA PAKE, SDEI).8 accepted
VMwareXXE injection in VGAuth SAML handling.1 accepted
RootstockPowHSM Merkle-proof verification bypass in sidechain federation key management.1 bounty (Immunefi)
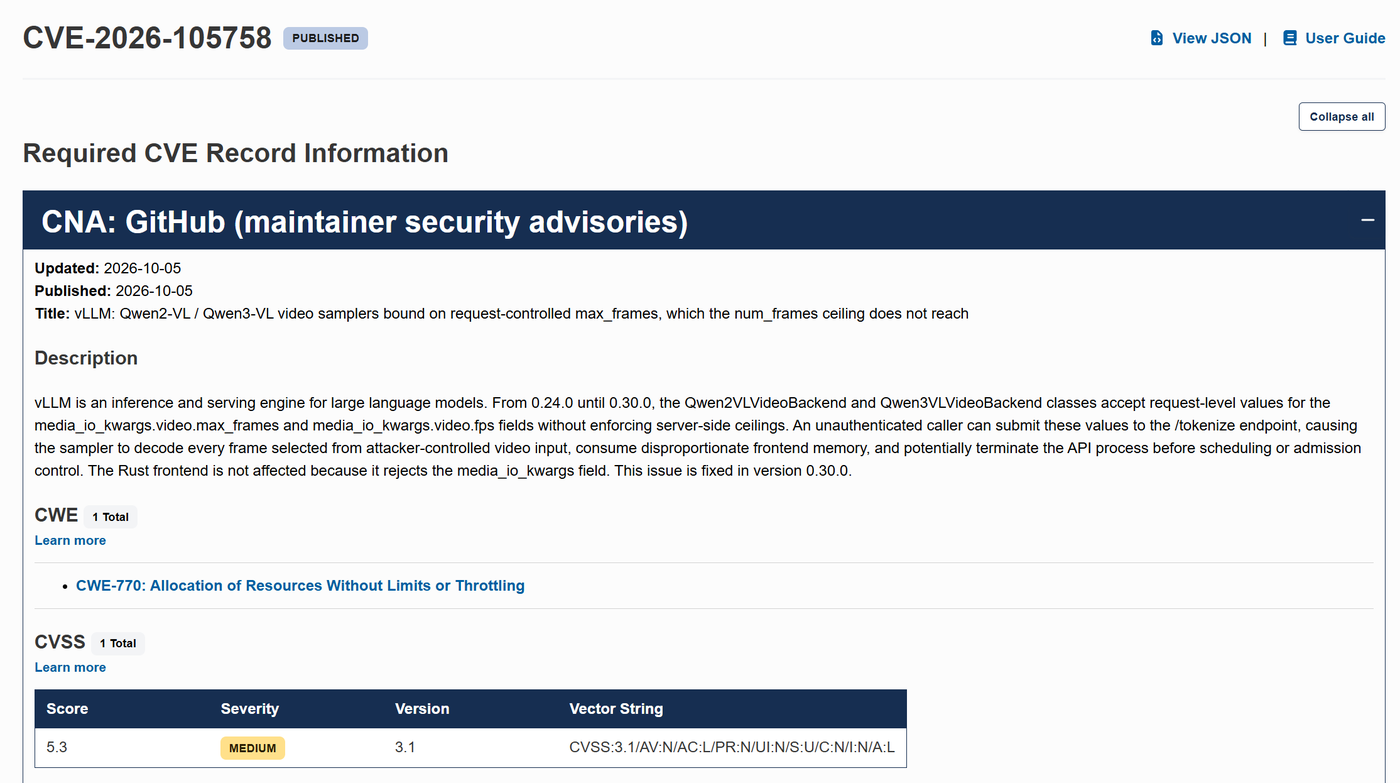
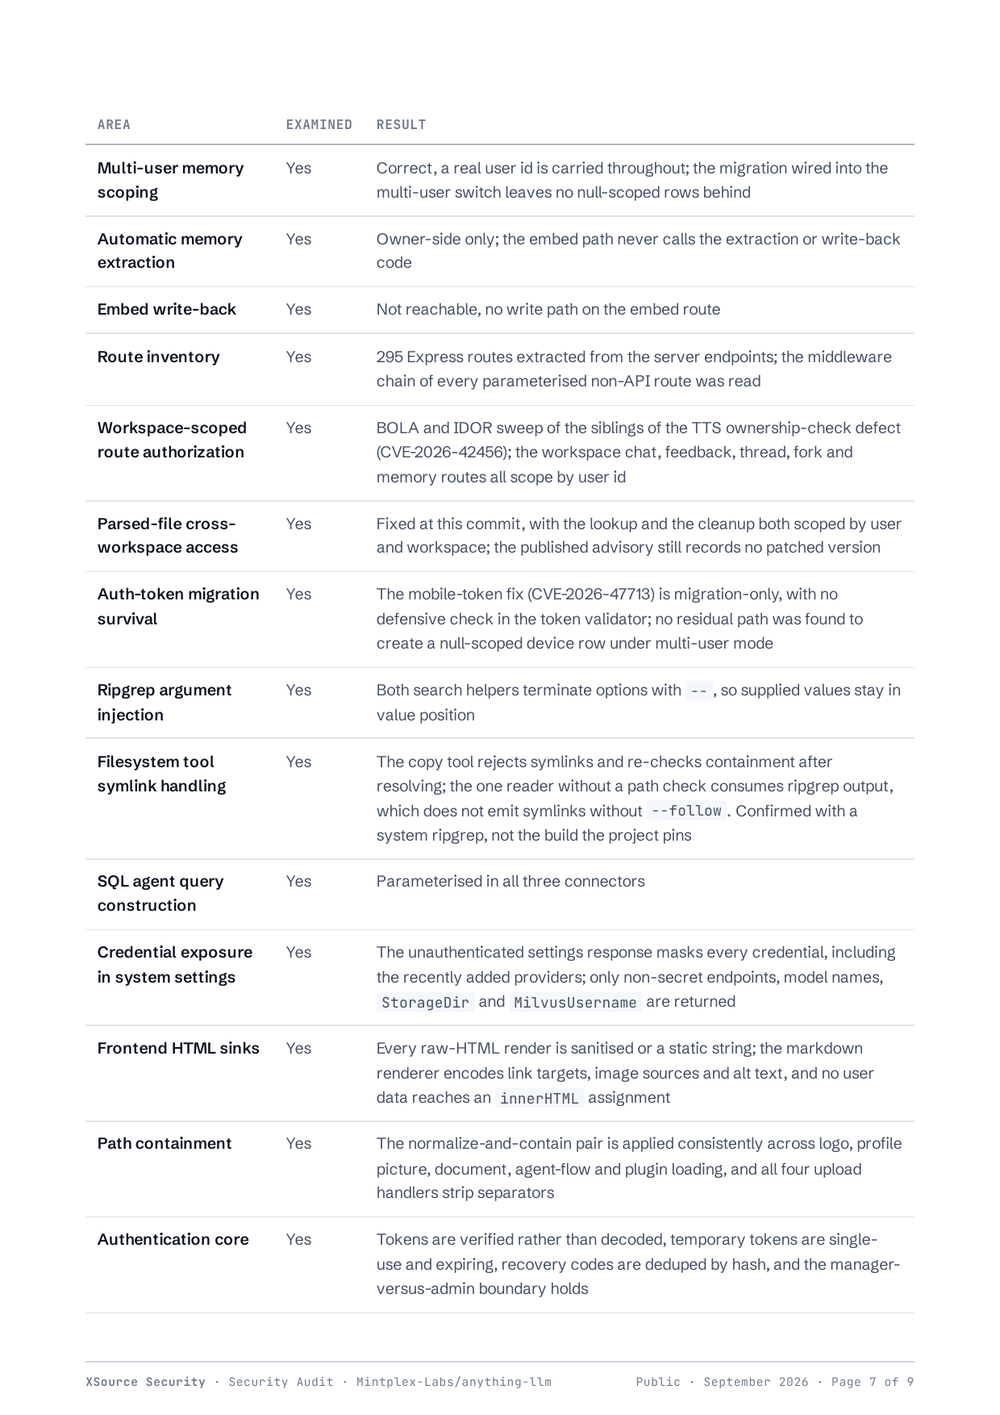
vLLMInference server: the Qwen2-VL and Qwen3-VL video samplers bound on a request-controlled frame count the server-side ceiling does not reach, so one unauthenticated request to /tokenize exhausts API-server memory. Fixed in v0.30.0 (GHSA-x6mc-67gf-chw4).CVE-2026-105758 AnythingLLMAnonymous embed-widget visitors received the instance owner's private memories in the system prompt (GHSA-8wh8-3v68-whwj).published advisory AI/ML toolingUnsafe deserialization, model-loading flaws, SSRF, path traversal and memory-safety issues across PyTorch, TensorFlow, OpenVINO, ExecuTorch and TVM.coordinated disclosures